
Exam Name: Certified Kubernetes Security Specialist (CKS)
Certification Provider: Linux Foundation
Corresponding Certification: Kubernetes Security Specialist

Over 58963+ Satisfied Customers
CKS Online Test Engine
- Online Tool, Convenient, easy to study.
- CKS Practice Online Anytime
- Instant Online Access CKS Dumps
- Supports All Web Browsers
- Test History and Performance Review
- Supports Windows / Mac / Android / iOS, etc.
- Try Online Engine Demo
- Total Questions: 66
- Updated on: Oct 27, 2026
- Price: $69.00
CKS Desktop Test Engine
- Installable Software Application
- Practice Offline Anytime
- Builds CKS Exam Confidence
- Simulates Real CKS Exam Environment
- Two Modes For CKS Practice
- Supports MS Operating System
- Software Screenshots
- Total Questions: 66
- Updated on: Oct 27, 2026
- Price: $69.00
CKS PDF Practice Q&A's
- Printable CKS PDF Format
- Instant Access to Download CKS PDF
- Study Anywhere, Anytime
- Prepared by Linux Foundation Experts
- Free CKS PDF Demo Available
- 365 Days Free Updates
- Download Q&A's Demo
- Total Questions: 66
- Updated on: Oct 27, 2026
- Price: $69.00
Instant Download Linux Foundation : CKS Exam Dumps

Updated: Oct 27, 2026
No. of Questions: 66 Questions & Answers
Download Limit: Unlimited
Instant Download: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
100% Money Back Guarantee
ActualTestsIT has an unprecedented 99.6% first time pass rate among our customers.  We're so confident of our products that we provide no hassle product exchange.
- Best exam practice material
- Three formats are optional
- Learn anywhere, anytime
- 100% Safe shopping experience
- 10 years of excellence
- 365 Days Free Updates
Time is money, especially in 2026. The Linux Foundation Certified Kubernetes Security Specialist (CKS) study engine from ActualTestsIT enormously saves the former — 66 practice questions for the CKS exam, ready in a minute.
Linux Foundation CKS Exam Syllabus Topics:
| Section | Weight | Objectives |
|---|---|---|
| Topic 1: Supply Chain Security | 20% | - Static analysis tools - Image security & scanning - Signed artifacts & verification - SBOM & CI/CD security - Permitted registries |
| Topic 2: System Hardening | 10% | - Least privilege IAM - Kernel hardening (AppArmor, seccomp) - Network access control - Minimize OS attack surface |
| Topic 3: Monitoring, Logging and Runtime Security | 20% | - Audit log configuration - Behavioral analytics - Incident investigation - Container immutability - Threat detection (Falco) |
| Topic 4: Minimize Microservice Vulnerabilities | 20% | - Pod Security Standards - Secret management - Security contexts - OPA/Gatekeeper implementation - Isolation & multi-tenancy |
| Topic 5: Cluster Hardening | 15% | - RBAC configuration - Component updates & vulnerability mitigation - API access restriction - Service account security |
| Topic 6: Cluster Setup | 15% | - CIS benchmark compliance - Network security policies - Secure Ingress configuration - Node metadata protection - Binary verification |
Linux Foundation CKS Exam: Quick Answers
Yes — download the free Linux Foundation Certified Kubernetes Security Specialist (CKS) demo and judge the quality yourself before paying; the whole content goes further than the demo, but the demo shows the style. Purchases include 365 days of free updates delivered by email; renew afterward at 50% off.
Must hold valid, non-expired Certified Kubernetes Administrator (CKA) certification Eligibility rules change over time, so verify the current requirements on the official page (official CKS exam page) before registering.
The Linux Foundation Certified Kubernetes Security Specialist (CKS) is Linux Foundation's certification exam for Certified Kubernetes Security Specialist (CKS), at the Professional level. Related credentials include Certified Kubernetes Administrator (CKA), Certified Kubernetes Application Developer (CKAD). Prepare efficiently: short review sessions anywhere, mock exams when you have a desk.
The Linux Foundation Certified Kubernetes Security Specialist (CKS) blueprint spans 6 domains — including Minimize Microservice Vulnerabilities (20%), Cluster Setup (15%), System Hardening (10%). Tag key points per domain in the PDF version; the complete outline above lists every subtopic.
120 minutes for 15-20 tasks questions. Build pacing with the ActualTestsIT software engine: repeated timed mock exams make the real clock feel easy.
Yes:
After any course, consolidate the knowledge with the 66 practice questions for the Linux Foundation Certified Kubernetes Security Specialist (CKS) — every answer expert-verified.
Our system emails the Linux Foundation Certified Kubernetes Security Specialist (CKS) material automatically right after purchase — about a minute; click the link, sign in, and use the engine immediately, with 24/7 help if nothing arrives within 2 hours. If you unfortunately fail the corresponding CKS exam within 60 days of purchase, you're welcome to a full refund: upload your failed result — a scanned enrollment slip plus the official Score Report PDF within 2 days of the exam — and we handle it within 7 days. Excluded: exams within 3 days of purchase, candidate names that don't match the payer, and free or expired products. We also recommend an alternative: exchange for two equal-value products free.
Through the vendor's official registration channels:
The Linux Foundation Certified Kubernetes Security Specialist (CKS) is delivered Online, remotely proctored, live monitoring via webcam and screen sharing — pick the arrangement that suits you when booking.
$445 USD per attempt, 67% to pass. Each retake costs the full fee, so prepare thoroughly the first time — the 66 practice questions for the CKS exam at ActualTestsIT closely simulate the real test.
Linux Foundation Certified Kubernetes Security Specialist (CKS) Sample Questions:
SIMULATION
A container image scanner is set up on the cluster.
Given an incomplete configuration in the directory
/etc/kubernetes/confcontrol and a functional container image scanner with HTTPS endpoint https://test-server.local.8081/image_policy
1. Enable the admission plugin.
2. Validate the control configuration and change it to implicit deny.
Finally, test the configuration by deploying the pod having the image tag as latest.
Correct Answer:
SeetheExplanationbelowExplanation:
ssh-add ~/.ssh/tempprivate
eval "$(ssh-agent -s)"
cd contrib/terraform/aws
vi terraform.tfvars
terraform init
terraform apply -var-file=credentials.tfvars
ansible-playbook -i ./inventory/hosts ./cluster.yml -e ansible_ssh_user=core -e bootstrap_os=coreos -b --become-user=root --flush-cache -e ansible_user=core
SIMULATION
You must connect to the correct host . Failure to do so may
result in a zero score.
[candidato@base] $ ssh cks000023
Task
Analyze and edit the Dockerfile located at /home/candidate/subtle-bee/build/Dockerfile, fixing one instruction present in the file that is a prominent security/best-practice issue.
Do not add or remove instructions; only modify the one existing instruction with a security/best-practice concern.
Do not build the Dockerfile, Failure to do so may result in running out of storage and a zero score.
Analyze and edit the given manifest file /home/candidate/subtle-bee/deployment.yaml, fixing one fields present in the file that are a prominent security/best-practice issue.
Do not add or remove fields; only modify the one existing field with a security/best-practice concern.
Should you need an unprivileged user for any of the tasks, use user nobody with user ID 65535.
Correct Answer:
See the Explanation below for complete solution
Explanation:
0) Connect to the correct host
ssh cks000023
sudo -i
PART A - Fix ONE prominent Dockerfile security/best-practice issue
1) Open the Dockerfile
vi /home/candidate/subtle-bee/build/Dockerfile
2) Find the "most obvious" security/best-practice problem and modify ONLY THAT ONE instruction Use / search in vi to quickly find candidates:
Candidate 1 (very common): USER root (or no USER but a USER 0)
Search:
/USER
If you see:
USER root
Change that single instruction to:
USER 65535
(or USER nobody if that exact word is already used in the file-but the task explicitly allows UID 65535, so USER 65535 is safest.)
✅ This is one-instruction change and is a top-tier best practice.
Candidate 2 (very common): FROM <image>:latest
Search:
/FROM
If you see something like:
FROM nginx:latest
Change ONLY that line to a pinned tag (example):
FROM nginx:1.25.5
(Any non-latest pinned version is the point. Don't add a digest line; just modify the existing FROM line.) Candidate 3: ADD http://... (remote URL download) Search:
/ADD
If you see remote URL usage like:
ADD https://example.com/app.tar.gz /app/
Change that single instruction to COPY only if it's copying local files.
If it's a remote URL, the more "correct" fix would normally be using curl with verification, but that would require adding instructions (not allowed).
So in this exam constraint, do NOT pick this unless it's actually a local add like:
ADD . /app
Then change just the word:
COPY . /app
3) Save and exit
:wq
Don't run docker build (task forbids building).
PART B - Fix ONE prominent security/best-practice issue in the Deployment manifest
4) Open the manifest
vi /home/candidate/subtle-bee/deployment.yaml
5) Change ONLY ONE existing field that is a clear security issue
Use / search in vi for the usual "bad fields":
Option 1 (most common): running as root
Search:
/runAsUser
If you see:
runAsUser: 0
Change that one existing field value to:
runAsUser: 65535
✅ This is a single-field change and matches the prompt hint.
Option 2: privileged container
Search:
/privileged
If you see:
privileged: true
Change only that value to:
privileged: false
Option 3: allow privilege escalation
Search:
/allowPrivilegeEscalation
If you see:
allowPrivilegeEscalation: true
Change only that value to:
allowPrivilegeEscalation: false
Option 4: writable root filesystem
Search:
/readOnlyRootFilesystem
If you see:
readOnlyRootFilesystem: false
Change only that value to:
readOnlyRootFilesystem: true
Option 5: image uses :latest
Search:
/image:
If you see:
image: something:latest
Change only that value to a pinned tag, e.g.:
image: something:1.2.3
6) Save and exit
:wq
What to pick (fast decision rule)
If you see run as root in either file, that's usually the highest scoring / most "prominent" security issue.
Dockerfile: USER root → USER 65535
Deployment: runAsUser: 0 → runAsUser: 65535
Those are perfect because you only modify one line/field and it matches the hint.
SIMULATION
Context
The kubeadm-created cluster's Kubernetes API server was, for testing purposes, temporarily configured to allow unauthenticated and unauthorized access granting the anonymous user duster-admin access.
Task
Reconfigure the cluster's Kubernetes API server to ensure that only authenticated and authorized REST requests are allowed.
Use authorization mode Node,RBAC and admission controller NodeRestriction.
Cleaning up, remove the ClusterRoleBinding for user system:anonymous.

Correct Answer:
See the Explanation below
Explanation:
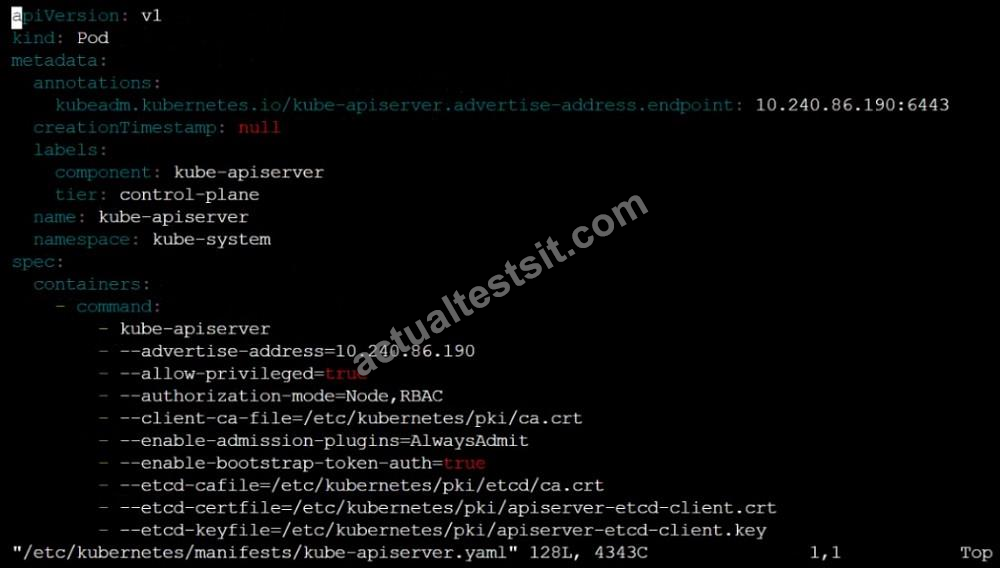


SIMULATION
Documentation Secrets, TLS Secrets, Volumes
You must connect to the correct host . Failure to do so may result in a zero score.
[candidate@base] $ ssh cks000m40
Path
Key
Context
You must complete securing access to a web server using SSL files stored in a TLS Secret .
Task
Create a TLS Secret named clever-cactus in the clever-cactus namespace for an existing Deployment named clever-cactus.
Use the following SSL files:
File
Certificate /home/candidate/clever-cactus/web.k8s.local.crt
/home/candidate/clever-cactus/web.k8s.local.key
The Deployment is already configured to use the TLS Secret.
Do not modify the existing Deployment.
Failure to do so may result in a reduced score.
Correct Answer:
See the Explanation below for complete solution
Explanation:
1) Connect to the correct host
ssh cks000m40
sudo -i
export KUBECONFIG=/etc/kubernetes/admin.conf
2) Verify namespace exists (quick check)
kubectl get ns clever-cactus
3) Verify certificate and key files exist
ls -l /home/candidate/clever-cactus/web.k8s.local.crt
ls -l /home/candidate/clever-cactus/web.k8s.local.key
Both files must exist.
4) Create the TLS Secret (THIS IS THE MAIN TASK)
Create a TLS Secret named clever-cactus in namespace clever-cactus:
kubectl -n clever-cactus create secret tls clever-cactus \
--cert=/home/candidate/clever-cactus/web.k8s.local.crt \
--key=/home/candidate/clever-cactus/web.k8s.local.key
Do NOT use apply
Do NOT edit the Deployment
5) Verify the Secret
kubectl -n clever-cactus get secret clever-cactus
Expected type:
kubernetes.io/tls
Optional detail check:
kubectl -n clever-cactus describe secret clever-cactus
You should see:
tls.crt
tls.key
6) (Optional) Confirm Pods are running
Since the Deployment is already configured to use the Secret, Pods should now work.
kubectl -n clever-cactus get pods
SIMULATION
Create a new ServiceAccount named backend-sa in the existing namespace default, which has the capability to list the pods inside the namespace default.
Create a new Pod named backend-pod in the namespace default, mount the newly created sa backend-sa to the pod, and Verify that the pod is able to list pods.
Ensure that the Pod is running.
Correct Answer:
A service account provides an identity for processes that run in a Pod.
When you (a human) access the cluster (for example, using kubectl), you are authenticated by the apiserver as a particular User Account (currently this is usually admin, unless your cluster administrator has customized your cluster). Processes in containers inside pods can also contact the apiserver. When they do, they are authenticated as a particular Service Account (for example, default).
When you create a pod, if you do not specify a service account, it is automatically assigned the default service account in the same namespace. If you get the raw json or yaml for a pod you have created (for example, kubectl get pods/<podname> -o yaml), you can see the spec.serviceAccountName field has been automatically set.
You can access the API from inside a pod using automatically mounted service account credentials, as described in Accessing the Cluster. The API permissions of the service account depend on the authorization plugin and policy in use.
In version 1.6+, you can opt out of automounting API credentials for a service account by setting automountServiceAccountToken: false on the service account:
apiVersion: v1
kind: ServiceAccount
metadata:
name: build-robot
automountServiceAccountToken: false
...
In version 1.6+, you can also opt out of automounting API credentials for a particular pod:
apiVersion: v1
kind: Pod
metadata:
name: my-pod
spec:
serviceAccountName: build-robot
automountServiceAccountToken: false
...
The pod spec takes precedence over the service account if both specify a automountServiceAccountToken value.
Viewing page 1 out of 14 pages.
Viewing questions 1-5 out of 66 questions.
 1063 Customer ReviewsCustomers Feedback (* Some similar or old comments have been hidden.)
This dumps is still valid in Spain. Nearly all questions can find from this dumps. you can depend on this without even fully study the course. Really valid dumps materials.
Scott
ActualTestsIT CKS real exam questions are still valid.
Gwendolyn
Best exam answers by ActualTestsIT for the CKS exam. I just studied for 2 days and confidently gave the exam. Got 98% marks. Thank you ActualTestsIT.
Theodore

All good, just passed CKS exam.
Otto

Very nice stuff, passed CKS exam today! But there are few new questions in the test. Just be careful and read carefully before answering.
Claire
I feel happy to cooperate with ActualTestsIT for I passed CKS with good score. So I commend ActualTestsIT to you.
Bing
You can pass the CKS exam only with this CKS preparation dump. It contains all the Q&A needed in the real exam. I got 93% marks.
Bertram
Finally achieved my destination with the help of ActualTestsIT Guide!
Quentin
Informed the CKS updated version is the latest. Thanks ActualTestsIT for making CKS exam possible. I scored 93% marks.
Phoebe
I passed my Linux Foundation Dynamics CKS exam by studying from ActualTestsIT. They have very informative pdf mock exams and testing engines. I scored 97%. Highly suggested
Sean
It was my passion to obtain Exam CKS and only ActualTestsIT worked for me.
Michael
I have failed once, this time I decide to choose the CKS dumps for help, lucky I passed it,you gays can rely on the ActualTestsIT.
Earl
I used ActualTestsIT CKS practice exam for CKS exam.
Eden
I have just purchased the CKS pratice questions and I am really amazed to see that it covers all the exam topics so briefly. Much recommended and worth buying.
Nigel
ActualTestsIT Questions and Answers format enabled me to learn the entire syllabus within days. The QandAs has the simplified information and was explained with the help of Hurrah! Secured a brilliant success in exam CKS!
Claude
Best exam answers for the CKS certification exam. ActualTestsIT is amazing. I scored 95% in the exam with the help of their sample questions.
Baird
Instant Download CKS
After Payment, our system will send you the products you purchase in mailbox in a minute after payment. If not received within 2 hours, please contact us.
365 Days Free Updates
Free update is available within 365 days after your purchase. After 365 days, you will get 50% discounts for updating.

Money Back Guarantee
Full refund if you fail the corresponding exam in 60 days after purchasing. And Free get any another product.
Security & Privacy
We respect customer privacy. We use McAfee's security service to provide you with utmost security for your personal information & peace of mind.
